FEC Faces Calls for Transparency After Cyberattack Shutdown
FEC cyberattack raises questions about transparency and accountability in election systems.
2 min read
The Federal Election Commission (FEC) is under increasing pressure to provide a full accounting of its response to a major cyberattack that caused a prolonged shutdown of its electronic filing services. The incident, which disrupted campaign finance filings for nearly 41 hours, has raised concerns about transparency, oversight, and the agency’s ability to protect election systems.
Quorum Crisis and Stalled Confirmations
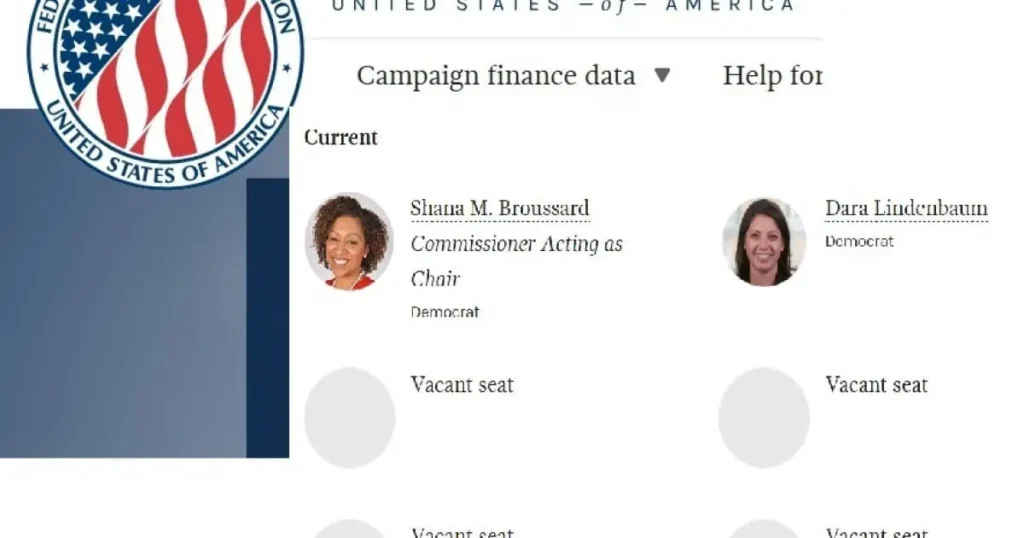
The FEC’s structure, designed to prevent single-party control, was severely impacted by a lack of a working quorum. Only two Democratic commissioners remained, leaving the agency without a Republican representative. This vacancy hindered decision-making, as major enforcement actions require four affirmative votes. President Donald Trump had nominated two Republican commissioners in 2026, but their confirmations stalled, raising questions about congressional oversight and the impact on the agency’s authority.
Cyberattack and System Outage
On October 26, the FEC took its electronic filing services offline, notifying campaign-compliance firms via email that a “bad actor” was attempting to breach systems. The service was restored nearly 41 hours later, but the public was not provided with a forensic account of the attack or evidence of containment. The duration of the outage and the attacker’s timeline remain unclear, with questions about when the breach began, how it was detected, and what access the attacker gained.
Security Warnings and Unresolved Risks
Despite prior warnings, the FEC’s systems remained vulnerable. An inspector-general report from December 2025 highlighted that while security controls were functioning as intended, they were insufficient to reduce breach risks. Legacy systems and budget constraints limited the ability to patch known vulnerabilities. Employees also reported fears of critical-system outages during campaign-filing deadlines.
Need for Detailed Response and Oversight
Experts and oversight bodies are calling for a detailed account of the response, including the email notification used to alert users, the steps taken to isolate systems, and the evidence collected during the incident. The FEC must provide a time-stamped record of its actions, including which systems were isolated, whether evidence was preserved, and who authorized the restoration of services. The public also demands clarity on whether the attack affected vote counts, with assurances that the final accounting must distinguish verified findings from unresolved questions.
Source: The Gateway Pundit